What UK clients, insurers and regulators ask about your people
Cyber Essentials, the UK GDPR, your cyber insurer and your clients' supplier questionnaires all ask, in their own way, whether your team can spot a scam. Here is what each one asks, and how scamcanary helps you show it.
Why it comes up
Phishing is by far the most common attack on UK businesses: 38% saw it in the past year, and 88% of the businesses that had a breach or attack were hit by phishing. Yet only 19% of businesses trained their staff on cyber security in that time (Cyber Security Breaches Survey 2025/26).
Cyber Essentials
Cyber Essentials is the minimum standard of cyber security the government recommends, and a growing number of organisations require suppliers to be certified to bid for work. Its requirements cover five technical controls: firewalls, secure configuration, security update management, user access control and malware protection (NCSC, Requirements for IT Infrastructure v3.3, April 2026). They don't ask for phishing training: the only staff education they mention is helping people choose good passwords. Training your team to spot a scam is the part Cyber Essentials leaves to you.
The UK GDPR and the ICO
Article 32 of the UK GDPR asks for appropriate technical and organisational measures to keep personal data secure. The ICO's own audit framework says that if staff training isn't appropriate for each person's role and the data they handle, this may breach UK GDPR articles 5(1)(f) and 32.
Insurers and clients
Cyber insurers and larger clients often ask for proof that staff are trained to spot phishing, in a renewal form or a supplier questionnaire. Almost half of UK businesses (47%) have some form of cyber insurance (Cyber Security Breaches Survey 2025/26), and an organisation with a turnover under £20m that certifies its whole organisation for Cyber Essentials is entitled to cyber liability insurance. If you supply IT services to essential services, watch the Cyber Security and Resilience Bill: it is not law yet, and the government plans for it to bring managed service providers under the UK's network security rules.
How scamcanary helps
- Practice phishing emails at five levels for everyone taking part, in the style of the UK brands and services your team deals with.
- Training modules in a set order, from passwords to what to do when something goes wrong, with privacy under the UK GDPR among them.
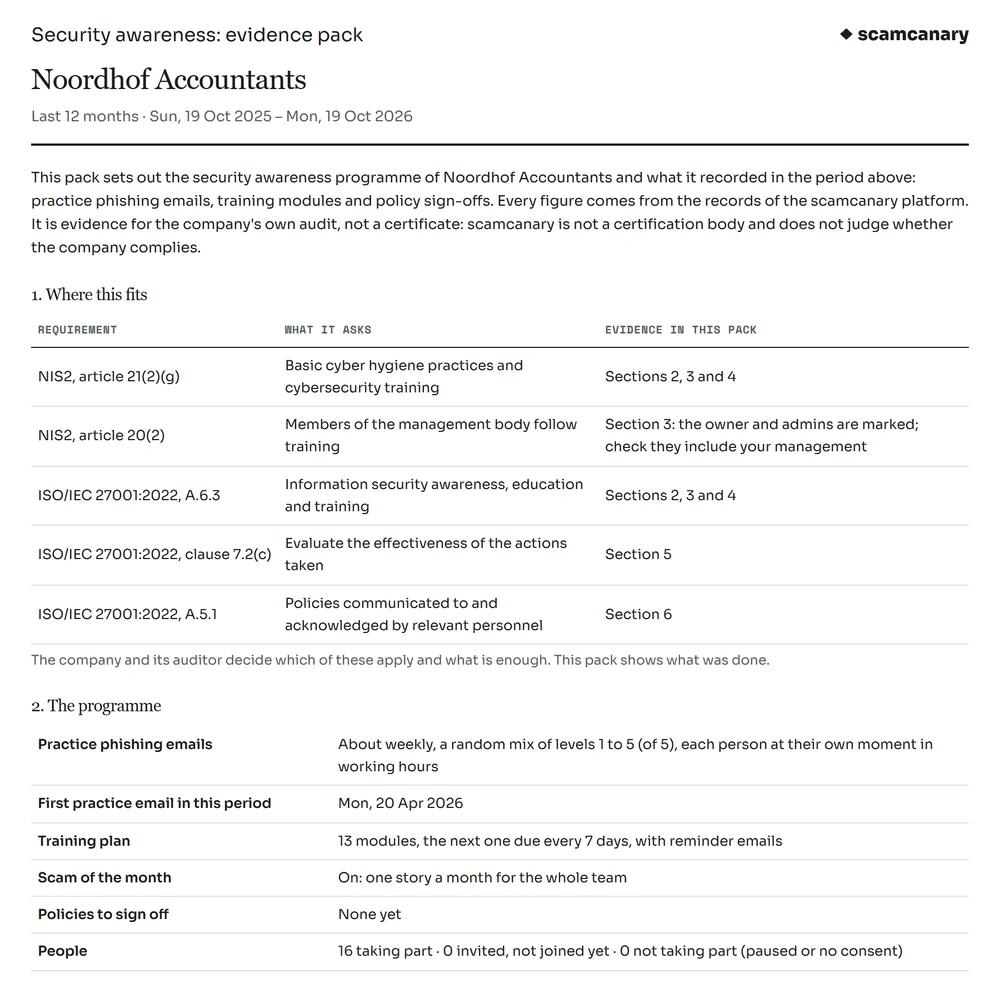
- An evidence pack for your auditor, insurer or client: the programme, the modules each person finished, practice emails and reports, whether it is working, and policy sign-offs.
- The pack shows where the programme fits the ISO/IEC 27001:2022 controls on awareness and training. Your auditor decides what is enough.
- Results per department and per level, ready when a client or insurer asks.
The free starting point
The NCSC's Top Tips for Staff is free e-learning that takes under 30 minutes, with phishing as one of its four topics. It is a good start. scamcanary adds what a one-off course can't: practice emails all year, a report button in Outlook, and a record of who did what.
What scamcanary is not
scamcanary is not a Cyber Essentials certification body, and it gives no certificate for Cyber Essentials, the UK GDPR or ISO 27001. Training is one measure among many: the technical controls, your policies and how you handle incidents matter just as much. What we give you is the evidence of what your team did.
Evidence your auditor can read
A printable pack for any period, one click from Reports & insights, with a CSV log of every practice email, finished module and policy sign-off behind it.
- Mapped to the ISO/IEC 27001:2022 controls on awareness, training and policies
- Who was trained on which module, when, and on which version
- Practice email results per level and per month
- Whether it works: click rates before and after the training
Evidence for your own audit, never a certificate. You and your auditor decide what is enough.
Cyber and data security, from passwords to ransomware. A game, not a slideshow.
Gamified modules in which you live through a situation and make the call. Your team gets them from the start and earns points for every module they finish. New modules are added regularly.
- First the story and your choice, then the explanation
- Easy for anyone to follow, no jargon
- Completion per person, as evidence for your audit
Need something specific? We’ll build it.
We adapt modules and practice emails to your sector, systems or policies, or create something new. That comes with a small quote, and is free with 25 or more people on an annual contract.
- A module on your own procedures
- Practice emails with your own systems and suppliers
- A country or language we don’t have yet
Practice is the best defence.
Start with your team today. The first round is ready within minutes.
Start freeOne platform, one price. No required annual contract, no credit card needed.
* The first 14 days are free. To continue after that, add your payment details: you then pay the price for your team size. Without them nothing is charged.