NIS2 asks for trained people. Here is how you show it happens.
NIS2 is an EU law on cybersecurity. If it applies to your organisation, directors must follow cybersecurity training, and training for everyone else is part of the measures you take. scamcanary provides that training and keeps track of who did what.
What is NIS2?
NIS2 is an EU directive from 2022 that raises the bar for cybersecurity. In the Netherlands it becomes law through the Cybersecurity Act (Cyberbeveiligingswet, Cbw). It covers far more organisations than the old rules: not only energy and drinking water, but also, for example, waste management, food production, digital services and many manufacturers.
Does it apply to you?
Usually, if you work in one of the sectors it lists and have 50 or more employees or more than 10 million euros in turnover. Some organisations fall under it whatever their size. Not sure? The Digital Trust Center explains who is covered, or ask your adviser. NIS2 is EU law: it does not apply to organisations that operate only in the United Kingdom, although insurers and clients there often ask for proof of training too.
What NIS2 says about training
- Directors must follow cybersecurity training themselves (article 20).
- Basic cyber hygiene and cybersecurity training are among the measures an organisation must take (article 21).
- Organisations are encouraged to offer their employees similar training regularly.
- Directors approve and oversee these measures, and can be held responsible for them.
How scamcanary helps
- Practice emails at five levels for everyone taking part, the board included.
- Modules on cyber and data security from A to Z, in a set order, from passwords to what to do when something goes wrong.
- Per employee you see which modules they finished and when.
- A certificate and a printable report as proof for your auditor or supervisor.
What scamcanary is not
NIS2 has no certificate, and scamcanary does not make you NIS2-compliant. The law asks for much more than training: risk management, reporting incidents, securing your suppliers. We take care of the training part, and of the proof that it happens.
Evidence your auditor can read
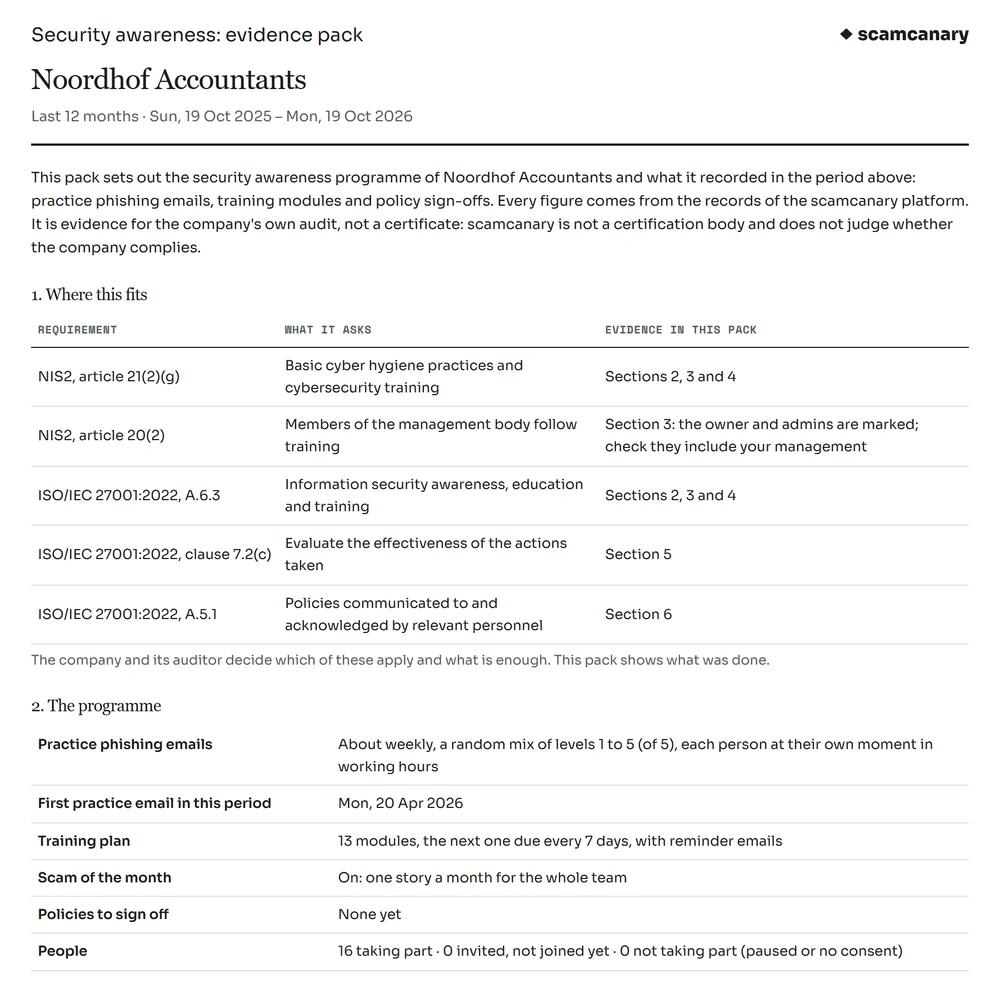
A printable pack for any period, one click from Reports & insights, with a CSV log of every practice email, finished module and policy sign-off behind it.
- Mapped to NIS2 article 21(2)(g) and 20(2), and to ISO/IEC 27001
- Who was trained on which module, when, and on which version
- Practice email results per level and per month
- Whether it works: click rates before and after the training
Evidence for your own audit, never a certificate. You and your auditor decide what is enough.
Cyber and data security from A to Z. A game, not a slideshow.
Gamified modules in which you live through a situation and make the call. Your team gets them from the start and earns points for every module they finish. New modules are added regularly.
- First the story and your choice, then the explanation
- Easy for anyone to follow, no jargon
- Completion per person, as evidence for your audit
Need something specific? We’ll build it.
We adapt modules and practice emails to your sector, systems or policies, or create something new. That comes with a small quote, and is free with 25 or more people on an annual contract.
- A module on your own procedures
- Practice emails with your own systems and suppliers
- A country or language we don’t have yet
Practice is the best defence.
Start with your team today. The first round is ready within minutes.
Start freeOne platform, one price. No required annual contract, no credit card needed.
* The first 14 days are free. After that your subscription starts automatically, at the price for your team size. Cancel free of charge up to and including day 14.